This guide explains how to add and configure your applications within AccessOwl. It also covers key concepts like bulk importing, assigning Business Owners/Admins, and using templates—without overriding any existing provisioning workflows you might have.
Officially managed by AccessOwl and visible in the app catalog for all employees. These apps include offboarding reminders and provisioning features.
Appear if AccessOwl detects usage through OAuth or domain sign-ups. They are not fully managed.
Mark an app as Managed if you want it tracked and controlled for user provisioning, offboarding, or audits.
Apps that are ignored won’t trigger revocation notifications when a user is being offboarded.
Mark an app as Ignored if it’s not used for typical business purposes, such as travel or lifestyle apps.
Apps your team has retired. Archiving an application revokes every current access on it and closes its pending requests. The access history stays available for audits.
AccessOwl can detect apps you use via Google Workspace OAuth logs. If an app doesn’t show in the list of discovered applications:
Create a custom entry: Manually add it in AccessOwl.
Use the built-in catalog: If the vendor exists in AccessOwl’s list, select it to speed things up.
You can still manage apps that don’t offer a direct integration. Instead of automatically provisioning user access it will notify the assigned application admins.
Only Org Admins can add an application to the catalogue and make it requestable. Application Admins and Business Owners manage applications that already exist, they cannot create new ones.
Integrated apps offer various functionalities like provisioning and user sync. If an app is already connected, hover over the “Connected” status icon to view the integration type.Two places on an application show capabilities, and they answer different questions. The Integration Capabilities box shows what your existing connection currently does, so a connection set up a while ago can show fewer capabilities than the integration supports today. The setup wizard, reached through the + on the application, shows everything the integration supports right now. If the wizard offers a capability your connection does not have, contact AccessOwl support to switch it on. It reuses the integration account already in place, so nothing needs reconnecting, and reconnecting does not add a capability by itself.
Hovering Connected on the Applications list shows the capabilities of that connection. Jira (Cloud) has Sync and Provisioning, 1Password has Provisioning only.
AccessOwl Integrations
Learn more about AccessOwl’s integrations.
Adding or integrating apps does not interfere with existing workflows in other provisioning tools such as Okta.
Your managed applications now include a filter for sync and provisioning integrations. Use this filter to narrow down your assigned apps by integration type, making it easier to see which of your managed apps are fully automated versus manually managed.
Every application carries a category, shown under its name on the Applications list. You can filter the Applications list by that category directly, for example to see only your Communication or Security apps.Tags cover what the fixed set of categories does not express. To group apps your own way, add tags to your applications (for example Eng tooling or Security) and use the Filter by tag dropdown on the Applications list.Tags are free-form labels you create directly on an application from its edit screen. To see all your tags and which applications carry each one, click Tags at the top of the Applications page.Programmatically, GET /api/v1/applications accepts a category_contains_word parameter that filters on the category directly. See List applications.
AccessOwl helps you manage vendor information by allowing you to record details like risk levels, renewal dates, and compliance notes. Use the Vendor Details section to add key information such as SOC 2 status, data location, or contract details. This keeps all vendor and application data centralized for easier renewal decisions and audits.To store additional information, such as user attributes, telephone numbers, or billing IDs, use the Markdown-enabled Notes field. You can also upload files like contracts or audit reports and bookmark important vendor URLs, ensuring all relevant details are easily accessible.
For integrations with user sync, AccessOwl updates user lists approximately every 3 hours.
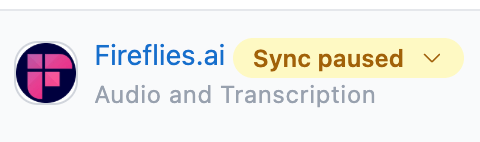
I see a connection error or a “Sync paused” status on an app. Is something wrong?
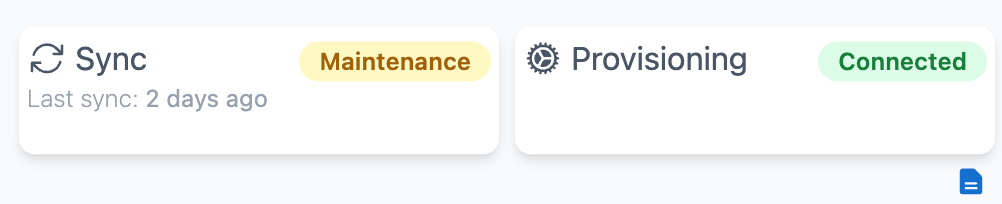
In most cases, no. Sync paused means AccessOwl has paused the user sync for this integration, usually because the integration is under maintenance on our side. Hover the status to see the capability cards. Sync shows Maintenance with the time of the last successful sync, while Provisioning keeps running, so access requests and revocations still go through. When there is more to say about the pause, the note appears in the connection details.The sync resumes on its own once the maintenance is done. There is nothing you need to do.
A broken authorization is the exception. If the app has stopped accepting the authorization AccessOwl connects with, retrying cannot fix it and the integration has to be reconnected. You do not have to go looking for it. AccessOwl shows an alert on the dashboard when an integration’s authorization breaks, and for Google Workspace, Microsoft 365 and GitHub your Org Admins also receive a Slack message with a Reconnect button and a link to the reconnection steps. For every other integration, the dashboard alert is where you find out. See Connection errors.When you open the integration, you’ll see status indicators in two places:
The status on the left is the integration’s overall connection state. A paused sync here resumes on its own. If the dashboard is instead showing an authorization alert for this app, the integration needs to be reconnected.
The indicators on the right show each capability that is set up, such as Sync and Provisioning, along with the time of its last successful sync. For Google Workspace and Microsoft 365, this also includes the User Directory capability.
Why isn’t a specific application showing up in the list of discovered apps?
AccessOwl identifies apps through OAuth logs from Google or Microsoft. If an app doesn’t support these sign-in methods, it won’t appear in the discovered apps list. However, you can manually add it from the app templates or as a custom app.
Why is a permission missing from Manual access update?
Manual Access Update, at the top of an application’s page, updates access a user already holds, for example correcting a role. The permission picker only lists permissions currently granted, so a permission the user has never held, or one whose grant has ended, does not appear there.A grant can end through a user sync. When a sync runs, it removes any permission it does not find in the synced data and stamps Access Until on it. That date cannot be cleared, it is the record that the access ended.To add a permission a user does not hold, click New Access on the Manual Access Update screen, then select the users and the permission to add. To fill in permissions for many users at once from a file, use a user list import on the application (Edit, then Import).On an application with user sync, the Manual Access Update button is not shown on the application’s page. You can still reach the same screen from Reports, under Manual update. Select the application there and use New Access to record permissions for a Manual Resource, for example to fill in who already holds a manually managed license on an application whose sign-in is provisioned through an identity provider group.
How do I retire an application we no longer use?
Archive it. Archiving revokes every current access on the application in one step, so you do not need to revoke users one by one first.
Open the application and click Edit.
Set the status to Archived and save.
Check the Revocations tab. Every user who had access now shows a Revoked entry with the reason Application archived and no longer available.
For applications with an active integration, AccessOwl runs those revocations against the app, so the user accounts are deprovisioned automatically. For applications without an integration, the access is marked revoked in AccessOwl only. No removal task is sent to the Application Admin, so remove the accounts in the application yourself.
Mark as unmanaged does not retire an application. It moves the app back to Discovered, where it keeps its users and access records. If you marked an app as unmanaged and want it archived instead, move it back to Managed first, then archive it.
Archiving creates an access revocation for every user who currently has access to the application, closes every pending approval on it, and cannot be reversed from the app.
How do I stop an app being requestable without giving up management of it?
Open the application, click Edit, switch off Requestable and save. The app stays Managed, so its access list, offboarding and access reviews all keep working. It disappears from the App Hub and from Slack access requests, so employees can no longer request it.This is different from the two options covered above. Mark as unmanaged moves the app back to Discovered, where it is no longer managed at all. Archived revokes every current access on the app. Neither is what you want when the goal is only to stop requests.There is no bulk edit for this setting, so switch it off one application at a time.
Did AccessOwl deactivate this user, or did it just record it?
AccessOwl only removes access when there is an access revocation or an offboarding behind it. Both are visible on the application’s Revocations tab and in the audit trail. If a deactivation has no matching revocation, AccessOwl did not do it.Everything else is observation. When an integration syncs the user list, it records access it can no longer find and stamps the date it noticed the change, which is the date shown under the user’s Deactivated section. That deactivation happened in the application itself or in the identity provider that manages it.A useful sanity check is the timestamp. Many accounts recorded as deactivated at the same moment point at a bulk change in the app or an identity provider run, not at AccessOwl, which only acts on individual revocations and offboardings.
How do I bulk revoke access to a specific app for multiple users?
If a team stops using an application and you want to remove access for several users at once:
Open the application page in AccessOwl.
Go to the Assigned Users tab.
Select the users you want to remove.
Click Revoke Access.
This removes access for all selected users in one action. For apps with an active integration, the revocation happens automatically. For apps without an integration, the application admin is notified to handle the removal.
Can I move all Discovered users to Assigned at once?
Yes. Open the application and go to the Discovered Users tab. Tick the checkbox in the table header to select every discovered user, or tick individual rows for a subset. Click Set Access and choose the access to assign. This promotes all selected users from Discovered to Assigned in one step.
How do I export a list of applications and who has access to them?
You have three options depending on what you need:
App inventory: On the Applications page, click Export in the top right. This gives you a single CSV covering every app, both managed and discovered, with app-level details such as status, user count, and costs. It does not include who has access or their permissions.
Who has access, across all apps: Go to the Reports tab in the admin interface and export the accesses report to CSV. This lists every access state org-wide, one row per access, including the permission level and whether it counts as elevated access. It covers both assigned access and access detected through shadow IT discovery.
Who has access, for a single app: Open the application, go to the Assigned Users tab, and click Export.
The access export from the Reports tab includes historical access states, so a department review can return rows for former users and access that has already ended. For a current-only list, filter out rows that have an end date populated (ended access), exclude Discovered apps, then filter by department. For programmatic exports, see the List access states API endpoint.