Capabilities
Provisioning
AccessOwl creates user accounts and assigns them to the specified groups during access requests.
Deprovisioning
AccessOwl removes users from your 1Password account during access revocations.
Prerequisites
- Membership in the Owners or Administrators group in your 1Password account, so you can invite the integration account and add it to the Administrators group.
- If your organization enforces Unlock with SSO, you’ll need to exempt the integration account from it. See Unlock with SSO below.
- If your organization uses 1Password firewall rules, they must not deny the Anonymous IP type Cloud Providers or the country Germany. See Firewall rules below.
Setup
1
Add 1Password in AccessOwl
Either add a new application or open Applications and click the +-symbol, then continue.
2
Invite the integration account
Follow the setup instructions in AccessOwl. You will be notified via Slack once the integration account’s initial setup is complete.
3
Add the integration account to the Administrators group
Wait for the Slack notification indicating the initial setup is complete before attempting to add the integration account to the Administrators group. Then, in 1Password, confirm the new user and add it to the Administrators group so it can manage other users.
The integration account is added to the Administrators group because that group grants the permissions to invite, suspend, and remove people, and to manage group memberships, which AccessOwl uses to provision and deprovision access.
4
Add 1Password groups manually (optional)
If you plan to provision 1Password groups, add them manually under the application’s permissions in AccessOwl.
Unlock with SSO
If your organization enforces Unlock with SSO, the integration account can’t sign in until you exempt it. AccessOwl signs the integration account in with its own account password and Secret Key. It can’t unlock through your identity provider the way a person does. While Unlock with SSO applies to the integration account, sign-in fails and provisioning can’t run. The exemption is configured on your 1Password side at the organization level, so AccessOwl can’t change it for you. Unlock with SSO is scoped by group, so the integration account needs to be in a group that is excluded from it.1
Create a group for the exemption
In 1Password, create a custom group, for example “No SSO”, and add the integration account to it. Make sure the integration account is in this group before it accepts the invite, otherwise it gets scoped into Unlock with SSO on sign-up.
2
Open the Single sign-on policy
Sign in to your account on 1Password.com, select Policies in the sidebar, then select Manage policies under Single sign-on.
3
Exclude the group
Under “Who can unlock 1Password with an identity provider”, choose Everyone except: groups you exclude and add your exemption group. If you already use Only groups you select, make sure the exemption group is not selected.
4
Save
Save the policy. The integration account keeps using the account password and Secret Key that AccessOwl manages, while the rest of your organization stays on SSO.
Members of the Owners group always unlock with their account password and are never scoped into Unlock with SSO. Adding the integration account to Owners is not recommended, since the Administrators group already grants the permissions AccessOwl needs.
Firewall rules
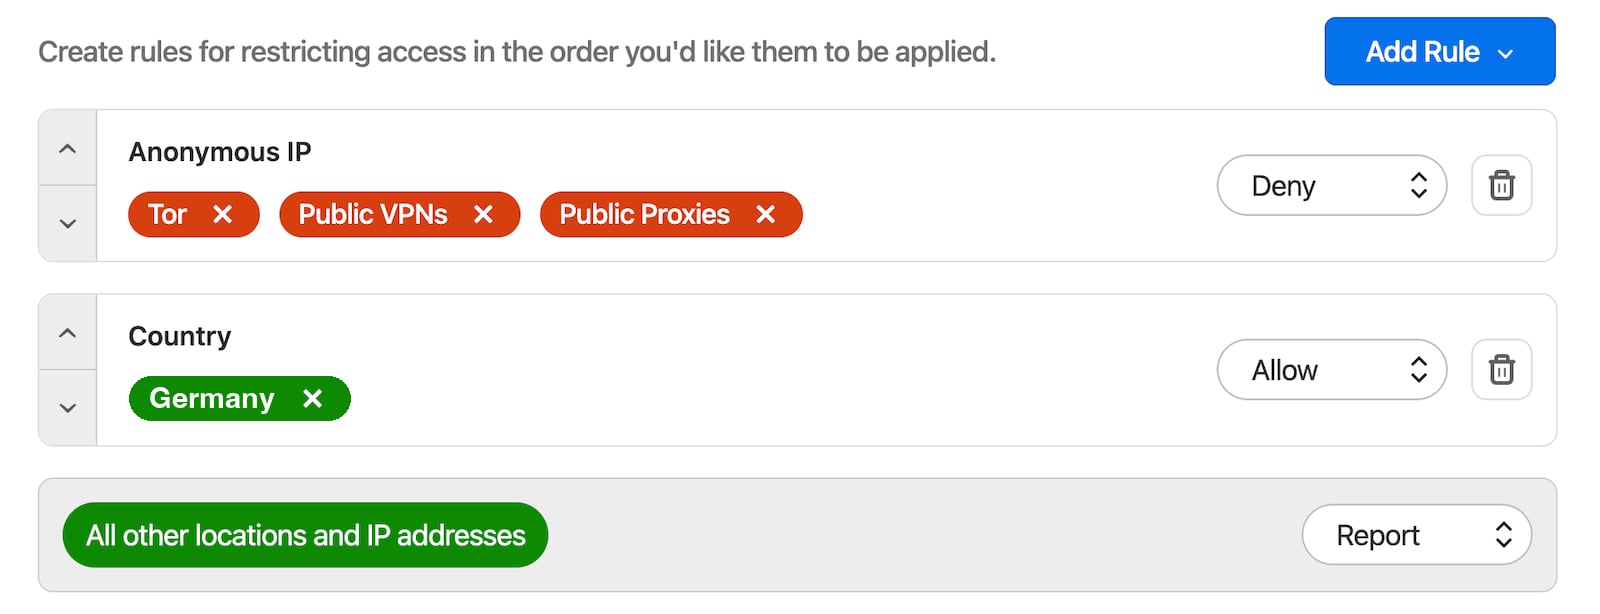
1Password Business lets you restrict where your team can sign in from. Firewall rules can deny sign-ins by country, continent, IP address, or by Anonymous IP type (Tor, Public VPNs, Public Proxies, and Cloud Providers). The integration account signs in from cloud infrastructure located in Germany. Two kinds of rules will block it:- A rule that denies the Anonymous IP type Cloud Providers
- A rule that denies the country Germany or the continent Europe
1
Open the Firewall policy
Sign in to your account on 1Password.com, select Policies in the sidebar, then select Manage policies on the Firewall policy.
2
Allow Cloud Providers
Open the rule that denies Anonymous IP addresses, select Anonymous IP, and remove Cloud Providers from the list. Tor, Public VPNs, and Public Proxies can stay denied.
3
Allow Germany
If you deny sign-ins by country or continent, make sure Germany and Europe are not on the deny list. Alternatively, add an allow rule for Germany above the deny rule.
4
Save and re-invite the integration account
Save the policy. If the invite already expired, re-invite the integration account.
Rules are applied in order and stop at the first match. An earlier deny rule wins over a later allow rule, so place any allow rule for Germany above the deny rules.
The egress IP addresses don’t apply to 1Password. It is an Agentic Integration and doesn’t connect from those addresses, so there is no IP address to allowlist.
FAQ
Access requests to groups are taking a long time
Access requests to groups are taking a long time
New 1Password users must accept the invite and complete the setup before they can be assigned to a group. The integration account checks at regular intervals to detect when the invitation has been accepted.
A request for a 1Password group was reassigned
A request for a 1Password group was reassigned
Whenever a user’s 1Password invite expires, AccessOwl automatically reassigns the outstanding access request for additional user groups. Resend the invite manually and speak with the user to ensure they accept it.